Bots Target BTCPay Servers Searching for Admin Keys
Automated systems are scanning exposed Bitcoin payment nodes, forcing users to patch their systems immediately.
 BTCcoinbeat.news
BTC/USD live chart
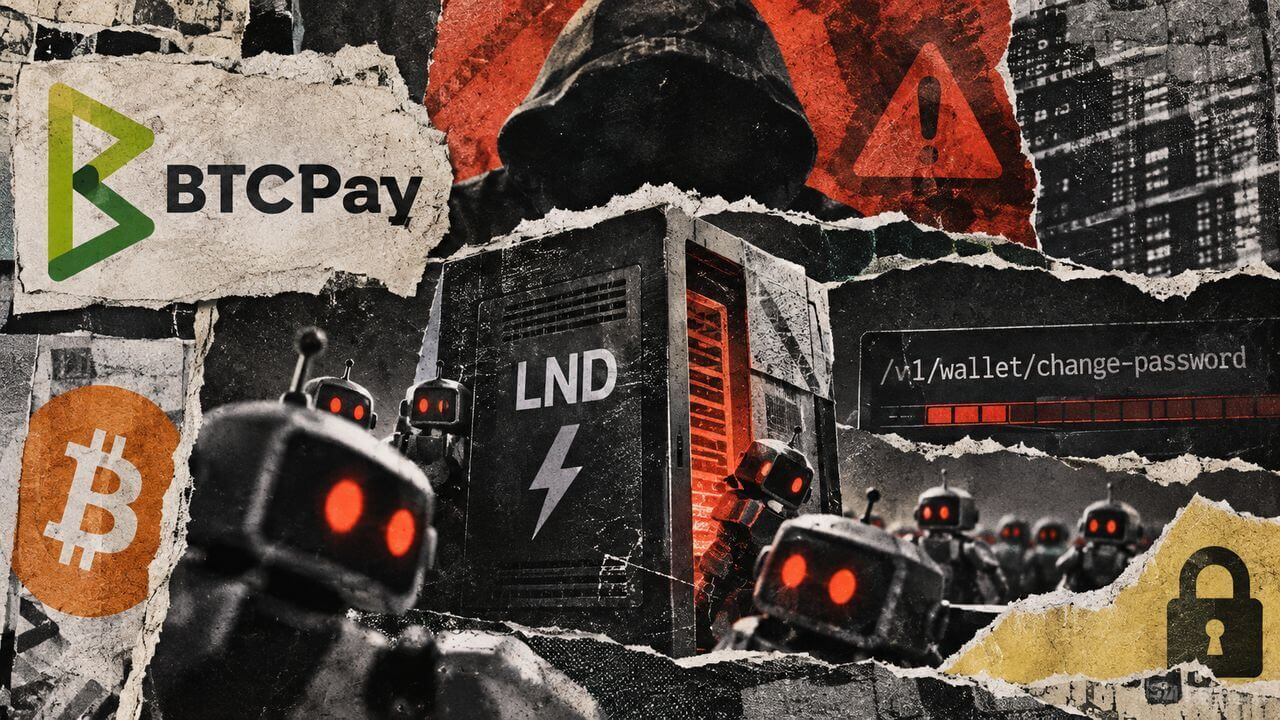
LIVEThe team behind BTCPay Server is warning users about malicious bots actively probing for vulnerable payment nodes. These automated systems are hunting for exposed servers to gain administrative control and potentially drain merchant wallets. This new threat follows a significant security breach last month that led to actual fund losses for some operators.
The issue centers on a brief window during node restarts when LND password protections can be bypassed. Bots are specifically targeting instances where operators manually enabled external access to their nodes, attempting to reset passwords and seize control. While this specific method is different from the August vulnerability, the end goal for attackers remains the same.
BTCPay has released version 2.4.4 to address these risks by mandating unique passwords and blocking unauthorized access methods. The update also migrates older installations to more secure configurations. However, these protections only work if the node is running the official BTCPay setup.
If you are running a custom deployment or have manually exposed your LND routes, your node remains at risk. Developers are urging all administrators to update their software immediately and remove any custom remote access routes that bypass standard security controls. Now is the time to audit your proxy rules to ensure your funds stay protected.
Prices update live from CoinMarketCap. Market data, not financial advice.
Market sentiment
Be the first to react
▍Comments (0)
No comments yet. Start the conversation!